Tóm tắt nội dung
Whoa!
I still remember the first time I plugged a Ledger into my laptop. It felt like locking a safe and handing away the key at the same time. My instinct said: this is the future of custody. Initially I thought hardware wallets were all about cold storage and nothing more, but then I realized staking changes the calculus—literally and emotionally. Something about delegating rewards while holding onto private keys felt both smart and a little unnerving…
Seriously?
Yes — seriously. Ledger devices let you sign transactions offline, which reduces attack surface in ways software-only wallets simply can’t match. On the other hand, staking often requires interacting with online validators or blockchains that push state back and forth, and that interaction introduces risks that aren’t fully solved by the device alone. I’m biased, but this part bugs me: people assume a hardware wallet is a magic shield and they stop doing basic hygiene. Hmm… proof of stake systems are attractive, but they demand operational care.
Here’s the thing.
Hardware wallets like Ledger Nano S and Nano X are designed to keep private keys inside a secure element, isolated from the host computer and the internet. That separation is genuinely powerful for preventing remote theft via malware. However, staking adds new vectors: you must approve delegations, unbonding requests, and sometimes smart contract interactions; those approvals are where social engineering and malicious UIs can trick you. On one hand, the device forces manual confirmation; on the other hand, users can still approve the wrong thing if the interface is misleading. Actually, wait—let me rephrase that: the device mitigates many threats but doesn’t replace user judgment or good tooling.
Wow!
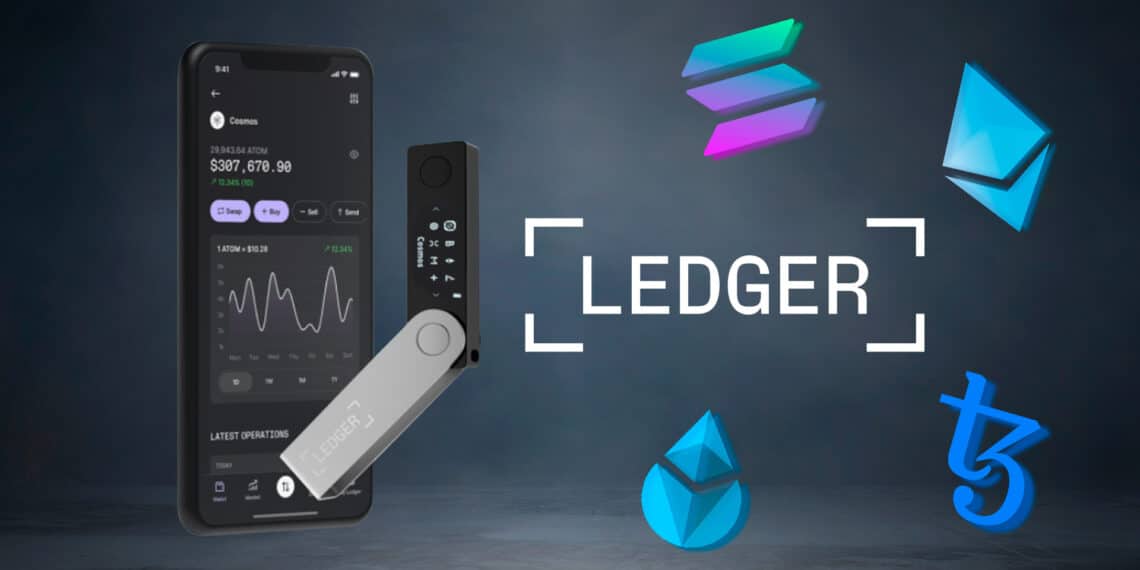
Okay, so check this out — Ledger’s ecosystem has matured. Their companion apps and integrations have improved, and the Ledger Live app (and yes, you can read more about their workflows at ledger live) are where most people begin. For staking specifically, some chains let you stake directly through Ledger Live while others require a third-party dApp or a full node; that diversity is both liberating and confusing. My experience is practical: for mainnet-native staking (Tezos, Cosmos, Polkadot variants), the fewer intermediaries the better. But every extra piece of software is another potential point of failure.
Hmm…
Let me get technical for a sec. When you stake with a hardware wallet, the private key never leaves the device; it signs an on-chain delegation transaction when prompted. That means an attacker who only controls your computer can’t forge withdrawals or steal keys without having physical access. Still, signing is an intentional act — you are telling the chain to lock or move funds, and if a malicious site manipulates the display or convinces you to sign a crafted payload, you could compromise funds or rewards. On the technical side, Ledger’s screen shows transaction details in a very specific format to reduce fraud, but screens are small and hard to read when complex contract calls are involved. So: the protection exists, but context matters.
Whoa!
Here are some practical steps from my day-to-day routine that help, and yes, I’m not perfect at these either. I always verify the receiving address and the exact amount on the device’s screen, not just on the computer. I maintain a separate, pristine machine for important operations when I’m doing big moves — that might sound extreme, but it’s saved me from odd browser extension issues. I also update firmware, though I know folks who hate firmware updates because of bricking fear; it’s a tension point. And somethin’ I repeat: never share your seed phrase, not even as a throwaway screenshot — double no.
Really?
On the topic of staking economics: staking rewards can be compelling, but there are trade-offs. Some chains have long unbonding periods; your funds might be illiquid for days or weeks if you need quick access. Slashing is another risk on some networks — validators can be penalized for downtime or misbehavior, and your delegated stake can lose a percent. Choosing reputable validators reduces slashing risk, though reputation is imperfect and changes over time. I tend to split stakes across multiple validators to balance yield and counterparty exposure.
Here’s the thing.
Validator selection should consider performance, commission, and community governance reputation — not just who pays the best immediate yield. Sometimes the highest APR is masking centralized power or long-term governance risks. Initially I chased the top yields, but then realized those validators often had operational shortcuts that made me uneasy. Now I palette it out: some aggressive positions for yield, and conservative ones for safety. It’s not one-size-fits-all, and your tolerance will differ from mine.
Whoa!
Now let’s talk UX pitfalls. The ledger device will show hashes and scripts that mean little to a human at a glance; you need tools that parse human-readable intent. A bad wallet UI can present “Approve transaction” without context, and you’ll hit confirm. I once nearly approved a contract call that had an extra and unrelated approval step embedded—luckily the device screen flagged the nonstandard data. That moment taught me a lot about vigilance. Oh, and by the way, always cross-check contract addresses on block explorers — yes, it’s tedious, but it’s smart.
Hmm…
Security also extends to backups and seed storage. Seed phrases are the last line of defense, and treating them as sacred is wise. I use a steel backup for my main seed and a separate paper for less critical accounts; others prefer multi-sig or split seeds. Multi-signature setups add complexity but can drastically reduce single-point failures; they also complicate staking in some ecosystems. On one hand, multi-sig improves custody; though actually, it makes on-chain operations clunkier and sometimes requires custom infrastructure.
Wow!
Emerging threats deserve mention. Supply chain attacks, counterfeit devices, and malicious firmware distribution are real albeit rare. Buy devices from authorized channels, check seals, and initialize them yourself. The Ledger company’s recovery and firmware procedures have evolved, and while not flawless, they show industry maturation. I’m not 100% sure any vendor is immune to novel attacks, but Ledger’s track record and a security-focused design make them a strong choice for many users.
Here’s the thing.
If you’re staking through a third-party service, consider custody and custodyless tradeoffs. Custodial platforms can offer convenience but they hold keys — that means systemic risk, they can be hacked, or they can freeze withdrawals. Noncustodial staking with a hardware wallet keeps control in your hands but requires more responsibility. For institutional actors, hybrid approaches and legal frameworks often change the calculus entirely. For everyday users, I lean toward noncustodial approaches with education and small, repeated operations until comfort rises.
Seriously?
Yes — seriously. My closing practical checklist is short and human, because long lists get ignored. 1) Buy hardware from a trusted source. 2) Verify device integrity and firmware. 3) Use Ledger and verified apps for basic staking flows. 4) Confirm every transaction on the device screen. 5) Diversify validators and split stakes. 6) Use durable seed backups and consider multi-sig if your assets warrant it. I’m biased toward safety and caution, and maybe that’s conservative, but it keeps crypto stress lower.
Quick FAQ
Can I stake directly from a Ledger device?
Yes, for many chains you can stake directly while keeping keys on-device, though some require a bridging app or third-party dApp. The essential point is that your private keys remain in the secure element while you sign staking or delegation transactions.
Is staking from a hardware wallet safe?
It’s safer than staking via a custodial exchange in many respects because you retain key custody. But it’s not risk-free: UI manipulation, malicious dApps, validator slashing, and human error remain possible. Use cautious validator selection and verify transaction details on-device.
Do I need Ledger Live for staking?
Not always. Some chains integrate into Ledger Live for a smoother experience while others rely on external wallet interfaces or command-line tools. Pick the path that balances convenience and security for you, and remember to verify everything on the device itself.